The Wire
FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports
CyberNews by Zentrya One
Section

Vulnerabilities

Disclosed flaws, patches and exploitation status.

critical CVE-2026-82533 Vulnerabilities

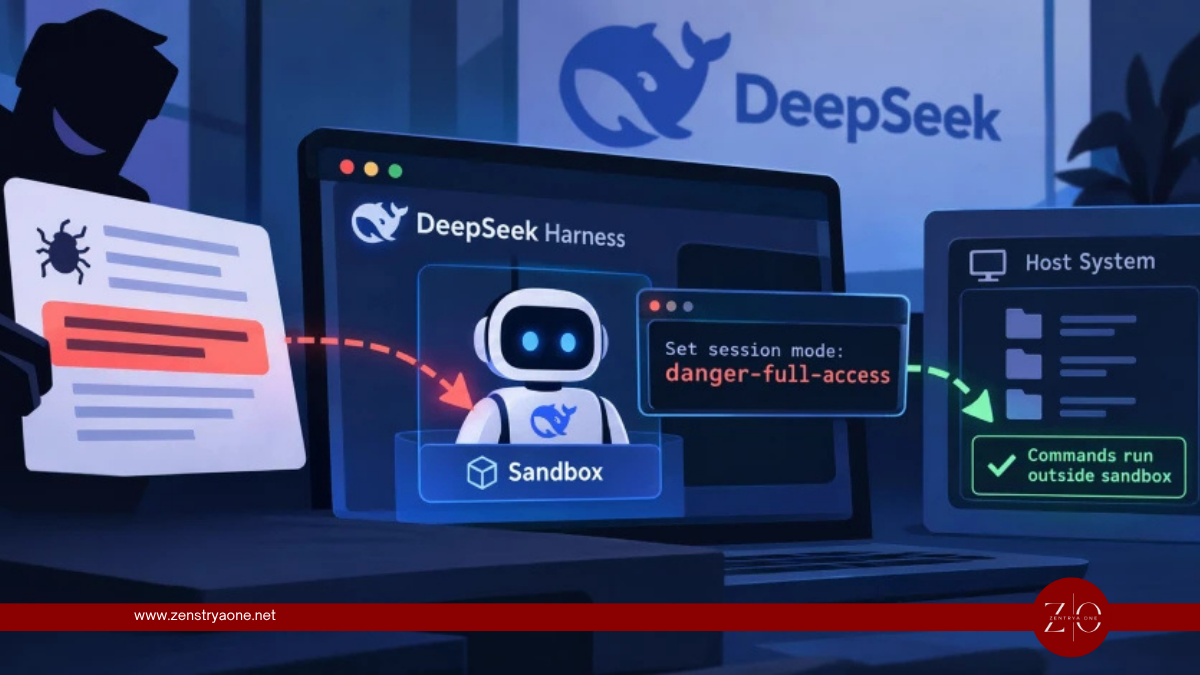
A Sandboxed AI Agent Could Switch Off Its Own Sandbox — and DeepSeek Harness Trusted It

CVE-2026-82533 carries a 9.4 severity score, and the mechanism is almost embarrassingly simple: the harness decided who to trust by reading a header the caller writes itself. Three weeks before the CVE landed, a developer had already posted a working reproduction on DeepSeek's own discussion board.
critical CVE-2026-44756 Vulnerabilities

SAP Fixes CVSS 10.0 OVERPASS Flaw Allowing Unauthenticated Remote Code Execution

SAP has released its September 2026 security updates, addressing multiple vulnerabilities across its enterprise software portfolio, including a maximum-severity flaw in the SAP Kernel that could allow unauthenticated attackers to remotely execute operating-system commands.

critical CVE-2026-69414 Vulnerabilities

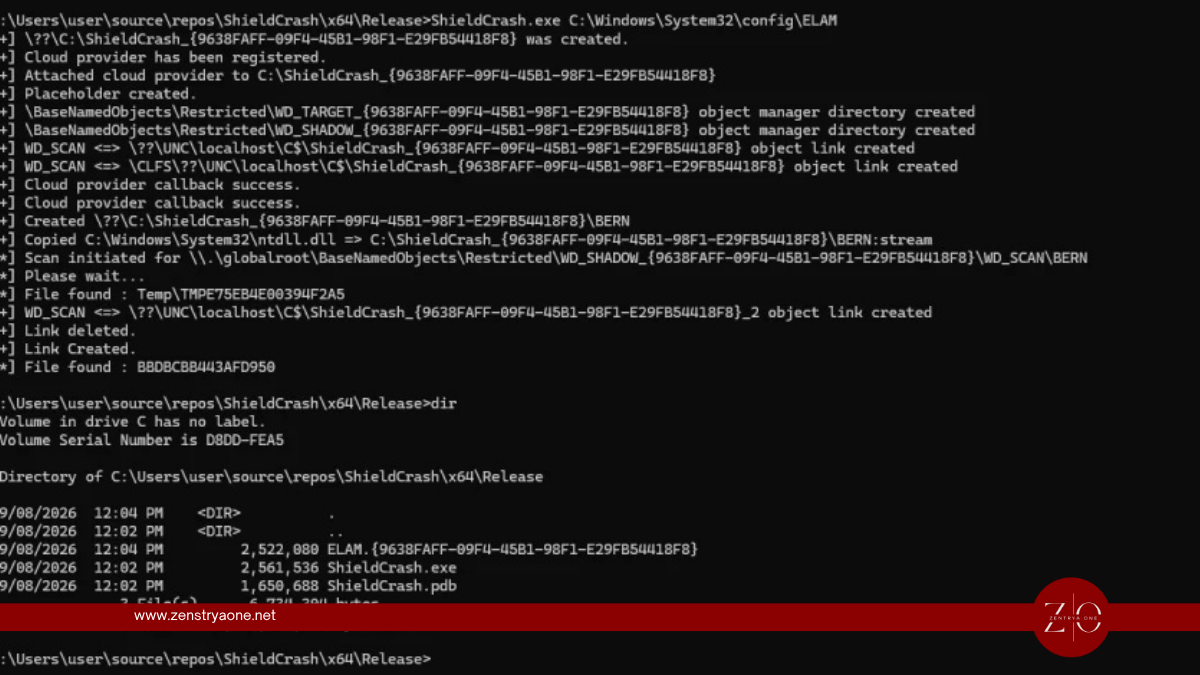
Microsoft Defender Patch Bypassed Again as New ShieldCrash PoC Emerges

A security researcher has released a new proof-of-concept (PoC) demonstrating that Microsoft's recent fix for a Microsoft Defender vulnerability known as **ShieldBreak** can reportedly be bypassed.

critical CVE-2026-86218 Vulnerabilities

N-able N-central CVSS 10 RCE Exploited in the Wild — Patch Immediately

A maximum-severity vulnerability in **N-able N-central**, a remote monitoring and management (RMM) platform widely used by managed service providers (MSPs) and IT teams, is now being exploited in the wild.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.