Cisco Warns of Critical ISE Zero-Day Exploited in Active Attacks
Cisco warns that CVE-2026-76460, a critical CVSS 10.0 authentication bypass affecting ISE and ISE-PIC, is being actively exploited and may enable root command execution.
Disclosed flaws, patches and exploitation status.
Cisco warns that CVE-2026-76460, a critical CVSS 10.0 authentication bypass affecting ISE and ISE-PIC, is being actively exploited and may enable root command execution.
Attackers are actively exploiting CVE-2026-89026, a critical Issabel Framework vulnerability that uses a hard-coded JWT signing key to enable unauthenticated OS command execution on vulnerable PBX servers.
Forever Security researchers showed how a browser extension could hijack AI assistants across Chrome, Edge, Perplexity Comet, Opera Neon and Claude, potentially accessing files and sensitive browser capabilities.
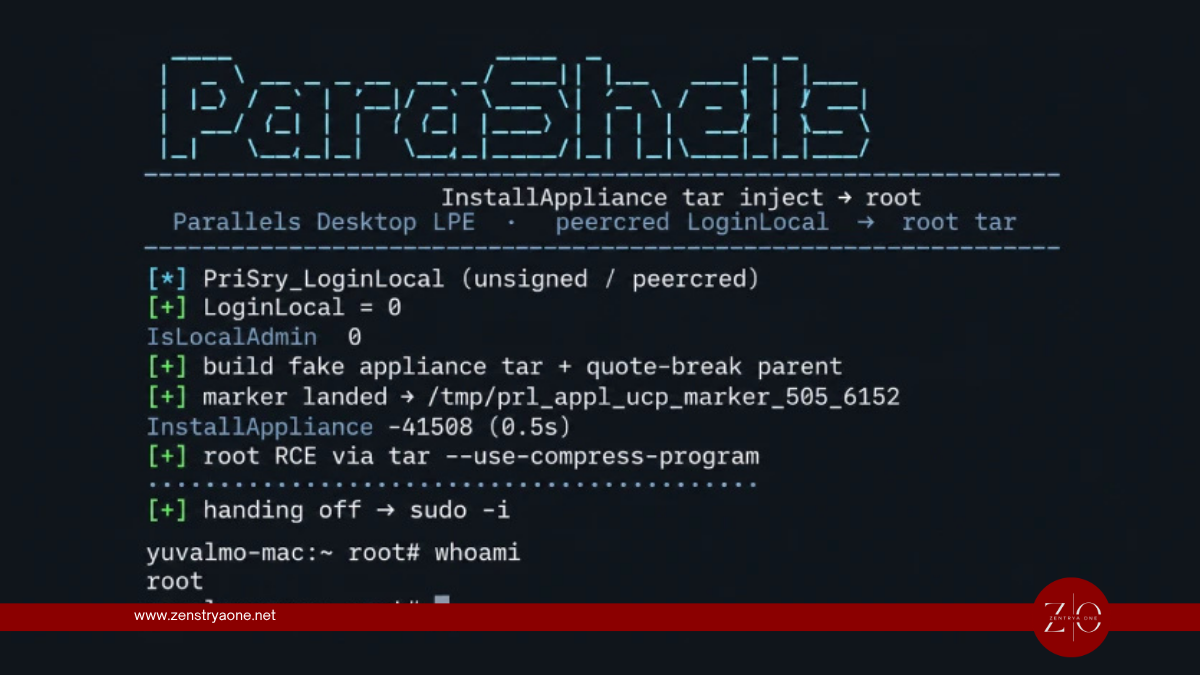
CVE-2026-90894, dubbed ParaShells, allows non-admin Mac users to exploit Parallels Desktop and execute code as root, while Intel Macs currently lack a confirmed fixed version.
Google patches CVE-2026-58704, a high-severity Pixel cellular modem vulnerability that requires no user interaction and shows signs of limited targeted exploitation.
Acronis has issued an urgent security update for a high-severity vulnerability affecting its Backup plugin for cPanel & WHM on Linux, after confirming that attackers have exploited the flaw in limited, targeted attacks.
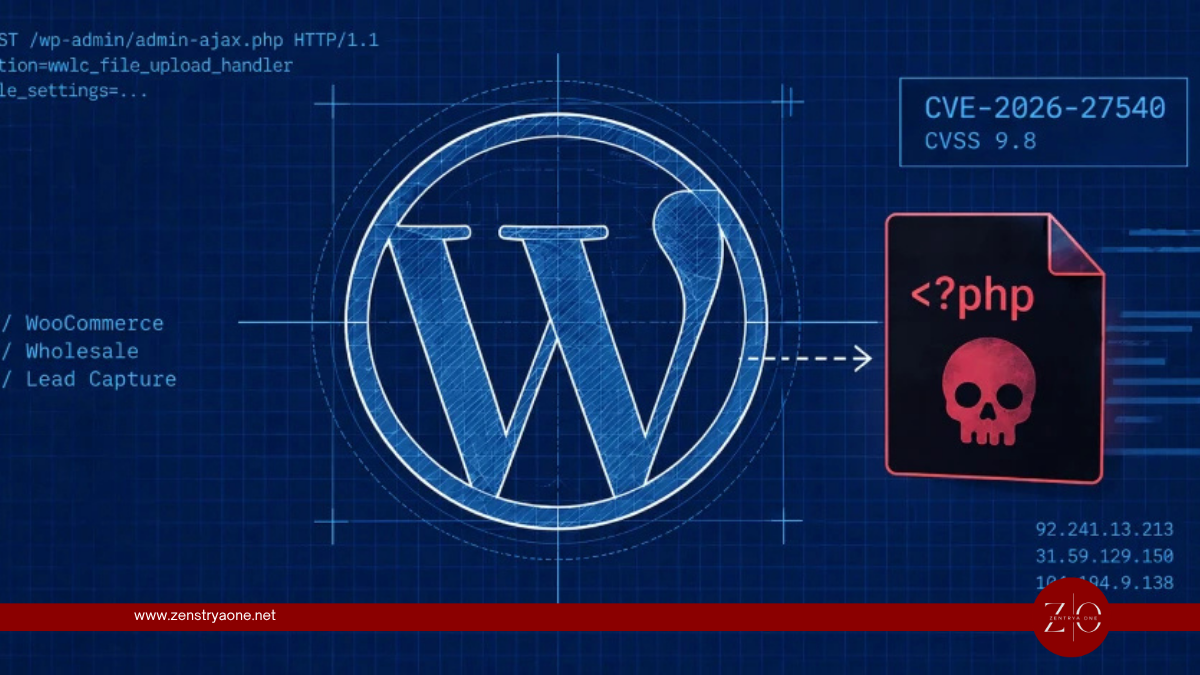
Threat actors are actively exploiting a critical vulnerability in the Wholesale Lead Capture Plugin for WooCommerce, allowing unauthenticated attackers to upload malicious PHP files and potentially take complete control of vulnerable WordPress websites.
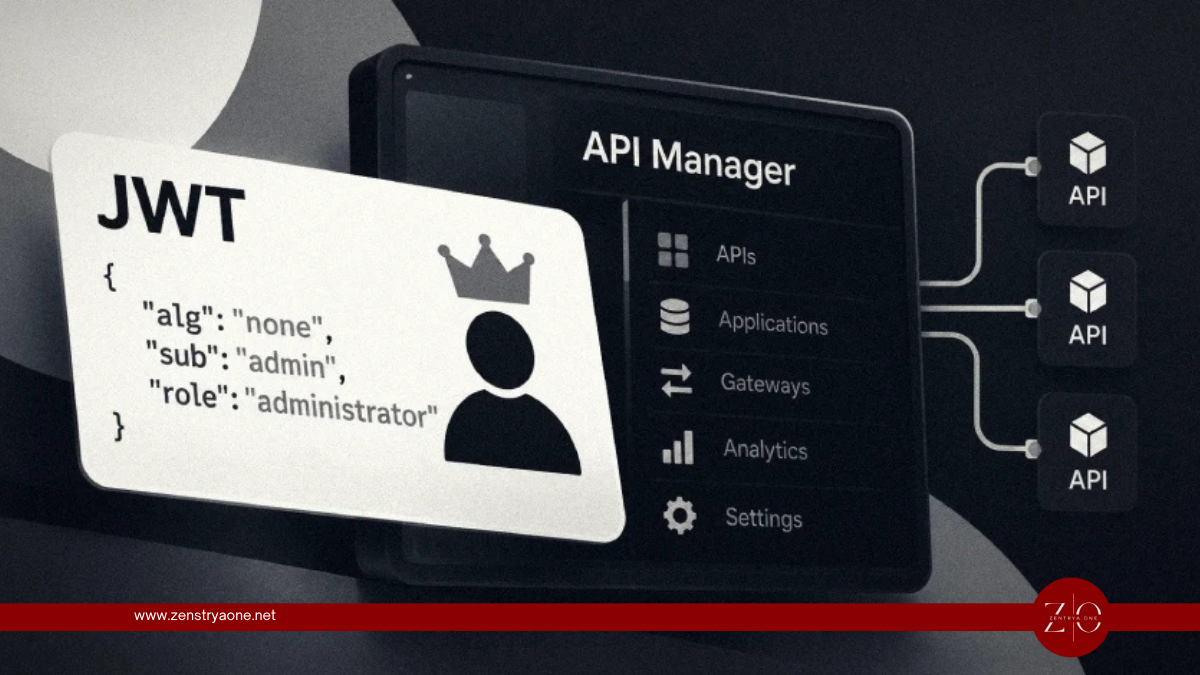
Security researchers have detected active exploitation attempts targeting a critical authentication-bypass vulnerability in WSO2 API Manager, with attackers sending forged JSON Web Tokens (JWTs) containing administrator privileges.
Nintendo has patched a high-severity vulnerability in the original Nintendo Switch that could allow a nearby attacker to execute unauthorized code or access information stored on the console.
China-linked threat actors have been observed chaining multiple vulnerabilities in Google Chrome and Microsoft Windows as part of sophisticated cyber-espionage campaigns targeting non-governmental organizations and other high-value organizations.
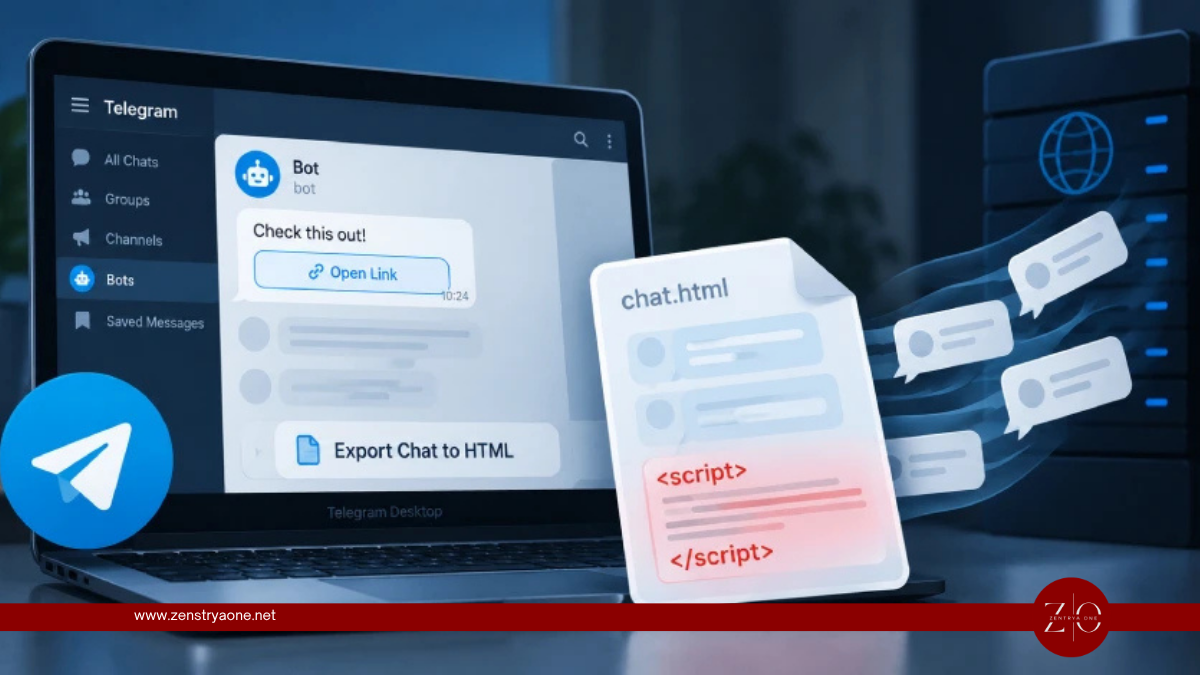
Security researchers have disclosed a high-severity vulnerability in Telegram Desktop that could allow malicious JavaScript hidden inside a seemingly normal chat message to execute when a conversation is exported as HTML and opened in a web browser.
A browser extension advertised as a Twitch enhancement tool has been found exposing users' OAuth session tokens to third-party proxy infrastructure, potentially allowing attackers to access affected Twitch accounts without knowing the users' passwords.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.