The Wire
FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports FILEDWeekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests CRITICALHackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure CRITICALAnthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities FILEDOver 100 Compromised Websites Spread LunexStealer Through Fake Cloudflare Verification Pages CRITICALEY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients CRITICALLibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings FILEDWikimedia Says ‘Rogue’ OpenAI Agents Tried to Exploit Tools and Generated Millions of Requests FILEDGoogle Pauses Open-Source Product Bug Bounties After Surge in Invalid Automated Reports
CyberNews by Zentrya One
Tag

Web Security

Every report filed under this tag.

critical CVE-2025-53521 Malware

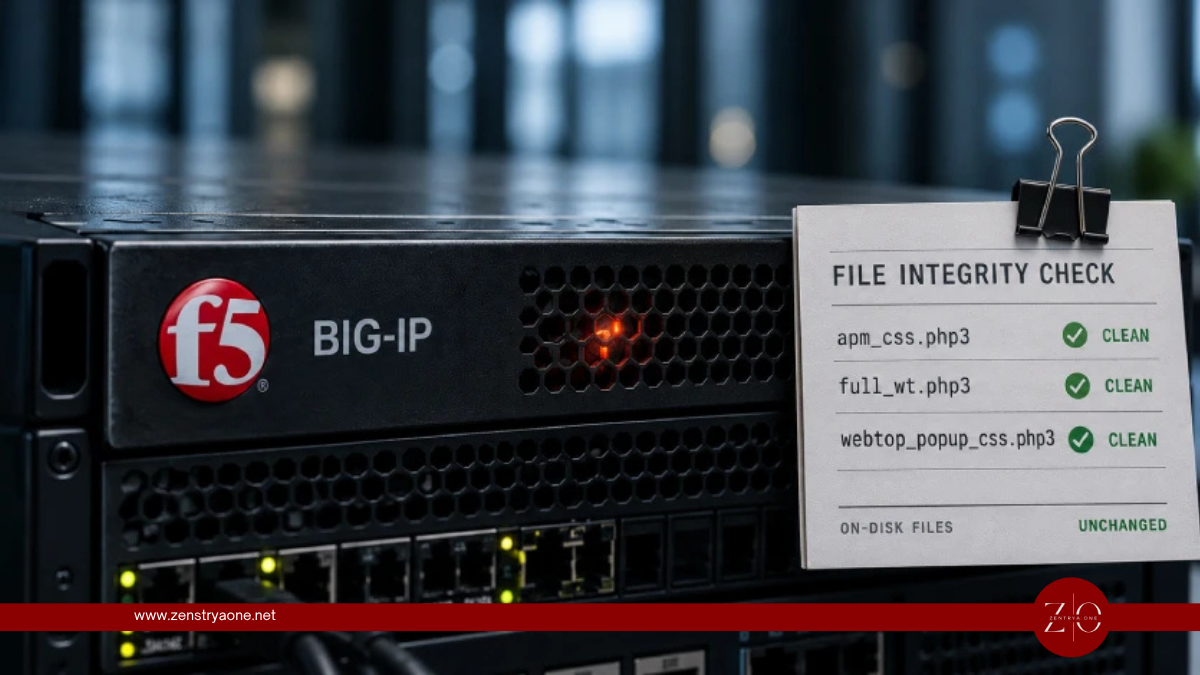
F5 BIG-IP APM Malware Hides Web Shell in Apache Memory to Evade Disk Scans

Security researchers have uncovered a sophisticated malware implant targeting F5 BIG-IP Access Policy Manager (APM) appliances that can conceal a PHP web shell entirely within Apache process memory, allowing attackers to maintain server-side code execution while leaving the targeted PHP files on disk unchanged.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.